
Migrate SharePoint permissions in 7 steps. Inventory, clean up, precreate, recreate levels, map, pilot and audit. Precreate users and groups first so every entry resolves. Build the identity mapping on user principal name. Pilot one site with real people before the full batch. Deny entries and root folder permissions do not migrate. RecoveryTools copies levels, groups and inheritance by user mapping.
What Happens to SharePoint Permissions Between Tenants?
Content and SharePoint permissions move as two separate things and only one of them is about files. The routes themselves are compared in how to migrate a SharePoint site to another tenant. Before you move anything, it pays to know what every permission level grants, which I explain in SharePoint permission levels explained.
A permission entry is a pointer. It names a user or a group in Entra ID and the role that identity has on a site, a library, a folder or one item. Copy the content to another tenant and those pointers come with it, still naming the source identities.
If the matching identity exists on the target, the pointer resolves and the person continues working. If it does not, the pointer resolves to nothing. The file sits there with no access and nothing in your migration report says so.

Every SharePoint permissions failure I have been called into was an identity problem wearing a content problem's clothes. The files were fine. The people were missing.
Jamie Kaler Marketing Head and Content Strategist, RecoveryTools
Why does Identity Mapping Decide SharePoint Permissions?
Microsoft is direct about the sequence. For a cross tenant SharePoint move, Microsoft states that all users and groups identified for migration must be precreated on the target tenant and the identity mapping file has to be uploaded to every target instance before content moves.
Base the identity mapping on something stable. User principal name for people, mail nickname for groups. A display name looks fine in a spreadsheet and breaks the moment somebody married, switched department or appears twice.
Four identity mapping mistakes cause most of the damage:
- A group that exists but is empty. It passes a spot check because the name matches. It grants nothing.
- A Microsoft 365 group that was never created. You lose more than SharePoint permissions. The team site, the shared mailbox and the Planner boards go with it.
- Duplicate identities from a second pass. Permissions split across two objects and the cleanup outlives the project.
- A parent group that is missing. Inheritance has nothing to inherit from so every site, library and folder below it loses access at once.
One licensing detail saves money here. Microsoft states that every user needs a license on either the source or the target tenant and the license does not have to be applied in both places.
Target Microsoft 365 groups have their own rule. Microsoft states they must be precreated in a specific way and that a target group for a group connected site cannot already be linked to an existing SharePoint site.
Which SharePoint Permissions do Not Migrate?
Most articles stop at "permissions are preserved". Microsoft's own documentation is narrower than that and the gaps are where access quietly disappears.
- Deny entries are dropped. Microsoft states plainly that special permissions, including Deny, are not saved. A person you deliberately blocked can arrive with access through a group.
- Inherited permissions are not copied. From a SharePoint source, only the unique permissions on a file migrate. Everything inherited is rebuilt by the destination instead.
- Custom permission levels are not listed as moving. Recreate them on the target before you migrate or every assignment pointing at them resolves nowhere.
- Root folder permissions can be skipped. When the destination is a document library, the source root folder permissions are not migrated.
- Sensitivity labels with user defined permissions block the move. Microsoft states sites holding them cannot be copied with a cross tenant move at all.
There is also a translation step. On premises Read becomes Read, Write becomes Contribute and Full control remains Full control. Anything outside those three has no equivalent waiting for it. Microsoft's own tool handles that route.
How Many Unique SharePoint Permissions can a Library Store?
Sources quote this number wrong constantly and the difference matters when you are sizing a project.
A list or library cannot store more than 50,000 unique security scopes. That is the hard platform ceiling. Separately, Microsoft recommends staying under 5,000 unique scopes per library when you migrate, because scopes above the list view threshold add database round trips that slow the transfer down.
Scope count drives cost as well as speed. Microsoft prices a permission call at five resource units against one for a file read, which is why a permissions heavy migration hits SharePoint move throttling sooner.
So 5,000 is advice and 50,000 is a wall. Plenty of blog posts report the advice as the wall, which makes a perfectly viable library look impossible.
Either way the fix is the same and it happens at the source rather than inside any tool. Replace per item sharing with group membership, let inheritance do its work again and the scope count falls on its own. Every folder shared with one person adds another scope.
Why can the Preserve Setting Overwrite Destination Permissions?
Here is the behavior that surprises people who did everything else right.
Switch the preserve user permissions setting on and point a migration at a library root and Microsoft documents what follows: the role assignments in the source root folder replace the role assignments of the target library. Use it at site level and a subsite becomes unique, with its own role assignments replaced by the source.
Replace, not merge. Any SharePoint permissions somebody built on the target before your migration are gone when the migration finishes.
That matters most on a phased move, where the destination has been live for weeks and an admin has already granted access to a few teams. Migrate into a subfolder rather than a library root when you need the target assignments untouched.
How do You Migrate SharePoint Permissions Step by Step?
Who it suits. Technical user (SharePoint admin or Entra ID admin) Source file size limit. Microsoft recommends under 5,000 unique scopes per library and sets the hard limit at 50,000 Extra application. Entra ID to precreate users and groups and a migration tool to open the identity map
Treat it as an identity project with a content phase bolted on. This order is what maintains access on the Monday after cutover.
- Inventory the permission model first. Count unique scopes per library, list every custom permission level and find the sites with broken inheritance. Numbers before plans.
- Clean up at the source. Remove departed accounts, collapse per item sharing into groups and delete obsolete groups. Migrating a mess reproduces the mess.
- Precreate users and groups on the target. Same membership, correct attributes, before any content moves.
- Recreate custom permission levels. Same names, same rights so the assignments have a destination.
- Build the identity mapping file on stable attributes. User principal name for people, mail nickname for groups and repeatable without creating duplicates.
- Pilot one site with real people. Three users, one guest and one departed account tell you more than a thousand files.
- Check effective access, not the report. Open the site as a mapped user and confirm what they can reach.
- Migrate in phases, then audit. Count scopes again at the destination and compare against the source inventory.
Map Your Identities Before You Move a Single File
Count permission scopes, custom levels and unmapped accounts across the estate first. Then test one site in the free trial before you plan the full batch.
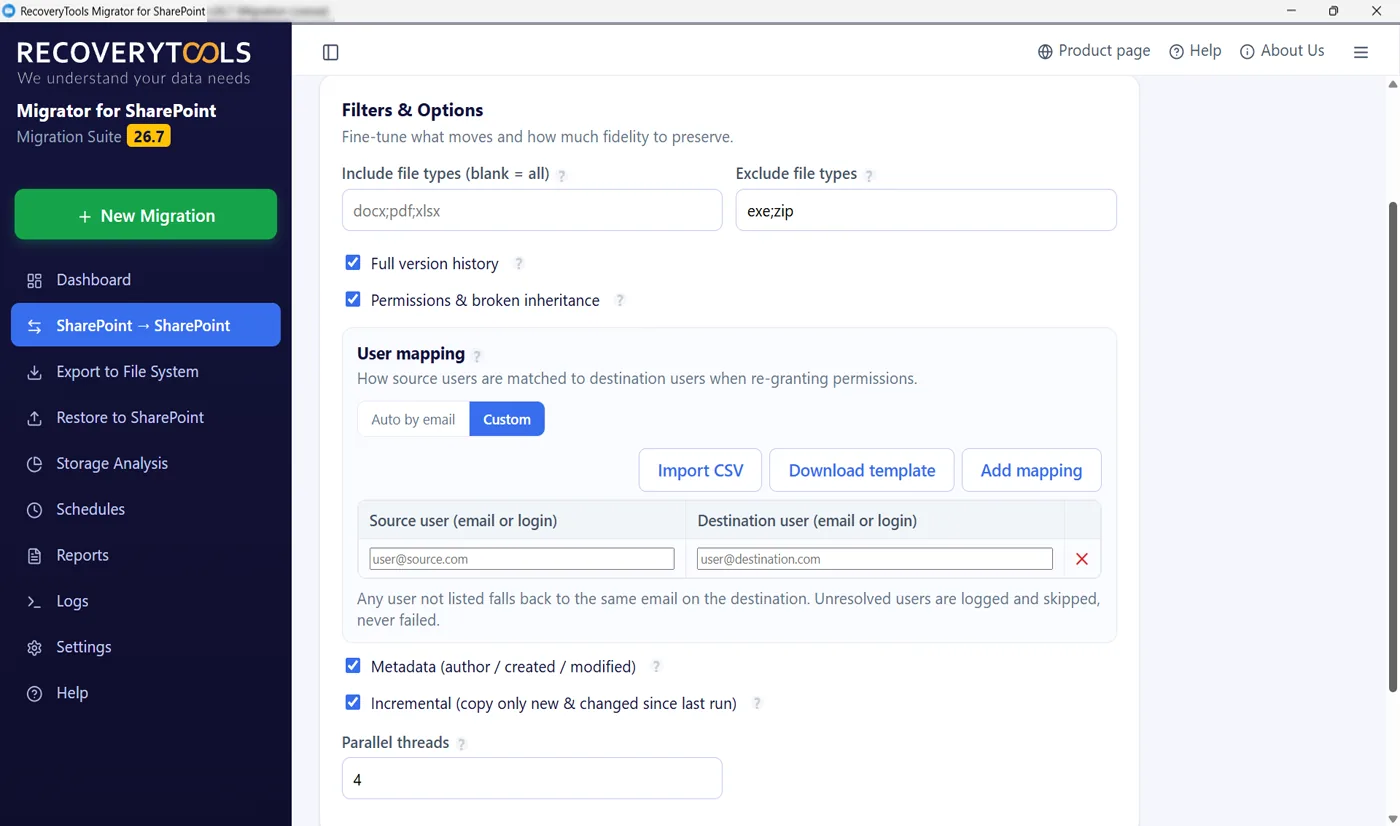
RecoveryTools SharePoint Migrator is an Easy to Use, graphical interface based utility. The software can map users from a CSV file and is able to carry permission levels, SharePoint groups and broken inheritance across. RecoveryTools allows you to schedule the transfer and the migrated data remains accessible with permissions and metadata retained.
Works on Windows 11, 10 and Windows Server 2022.
RecoveryTools SharePoint Migrator carries permission levels, SharePoint groups and broken inheritance across through the user mapping and the rest of the site moves in the same pass.
Does a Delta Pass Carry Permission Updates?
Not on its own and this one catches careful teams.
Microsoft states that on a delta sync, permissions migrate only when the corresponding files are transferred. A delta pass moves what differs and a permission edit is not a file edit.
Picture the gap. You start the bulk migration on Tuesday. On Thursday somebody at the source grants three people access to a contract folder, touching no file. Your delta pass on Saturday sees nothing to move so those three SharePoint permissions never arrive.
Freeze permission edits at the source once the bulk copy starts, the same way you freeze content edits. Collect any edits made during the window and apply them at the destination by hand.
What Happens to Permissions for External Guests and Sharing Links?
Guests are different in kind from everyone else. A guest is an invitation your tenant issued, not a person your tenant owns so a guest cannot be copied into another directory.
Sharing links are better news than most people expect. Microsoft states that when a cross tenant SharePoint site migration completes, existing shared links for the migrated files are redirected automatically. That promise belongs to the native route alone and the copy based routes behave differently, which is set out in what happens to SharePoint sharing links after migration.
Three things still need hands:
- Invite guests again on the target. Then map them so their SharePoint permissions have an identity to attach to.
- Compare external sharing policy on both tenants. A stricter destination locks out collaborators who worked fine yesterday.
- Review conditional access rules. Policies written against source objects do nothing useful on the target.
How do You Verify SharePoint Permissions After the Move?
A migration report lists what the tool did. Only effective access tells you whether people can work so check that instead.
- Sign in as mapped users. Three ordinary staff across three sites and confirm what all of them can open.
- Test one guest and one departed account. The guest should get in. The departed account should not.
- Open a broken inheritance folder. Unique SharePoint permissions are where the gaps hide, not on the site home page.
- Look for empty groups. A group with the right name and no members is the failure that survives every casual check.
- Count scopes at both ends. A destination library with far fewer scopes than its source lost assignments on the way.
Version history has its own trap after cutover, covered in SharePoint version history migration.
Frequently Asked Questions
Do SharePoint Permissions Migrate to Another Tenant Automatically?
No. Microsoft states that users and groups must be precreated on the target tenant and listed in the identity mapping file. Unmapped accounts produce permission entries that point at identities that do not exist so the content arrives without access.
Can a SharePoint Library Store 50,000 Unique Permission Scopes?
Yes. 50,000 unique security scopes is the hard limit per list or library. Microsoft recommends under 5,000 before a migration, because scopes above the list view threshold slow the transfer down.
Does a Migration Save Deny Permissions?
No. Microsoft states that special permissions, including Deny, are not saved. Check every Deny entry at the source before you move, because a person you blocked can arrive with access through a group.
Do Custom Permission Levels Migrate?
No. Microsoft does not list custom permission levels among the items that move. Recreate them in the destination tenant with the same names and rights before content moves.
Can You Check Effective Access After the Move?
Yes. Sign in as a mapped user and confirm what that person can open. A migration report lists what the tool did, while effective access shows whether people can work.
Do Shared Links Still Open After a Cross Tenant Migration?
Yes. Microsoft states that existing shared links for the migrated files are redirected automatically when a cross tenant site migration completes. Guests still need an identity on the target for those links to open.
Do Guests Need New Invitations After Migration?
Yes. Guests need fresh invitations in the destination tenant and then mapping. A guest is an invitation a tenant issued, not an account it owns.
Where to Start This Week
Count two things and your plan takes shape. Unique permission scopes per library and accounts with no match on the target. Both feed the timeline math in how long does a SharePoint move take.
The second number is the one that decides your timeline, because provisioning identities is work that cannot be rushed and cannot be done after the content moves. Everything else follows from getting the identity mapping right. Fold it into the wider Microsoft 365 migration planning checklist rather than treating it as a separate exercise.
Then ask the question that settles the rest. Who is missing on the far side and who is creating them?
Jamie blends strategic marketing insight with technical writing, turning migration and recovery topics into guidance that works for technical and general readers alike.
Published 7 October 2026. Permission behavior quoted above comes from file and folder permissions when migrating, permission settings in Migration Manager, cross tenant SharePoint site migration migration permission guidance, avoiding throttling in SharePoint Online.